TechBlonhub A new digital technology era.

One infected laptop should not be able to talk to your finance system, your IP cameras, and the conference room display all at once. That is the real reason people search for how to segment office network environments – not to make diagrams look cleaner, but to stop small problems from becoming company-wide outages or security incidents.
For most offices, segmentation is the line between a network that is merely connected and one that is actually manageable. If every device sits on the same flat network, troubleshooting gets messy, broadcast traffic spreads everywhere, and a compromised endpoint has far too much freedom. Segmenting the network limits that damage. It also gives you better performance control and a clearer policy for who and what should communicate.
What office network segmentation actually means
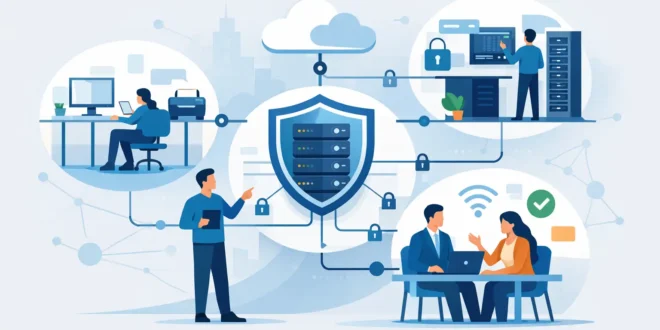
At a practical level, segmentation means dividing one office network into smaller, controlled sections. Those sections can be based on department, device type, trust level, or business function. Common examples include separate networks for staff computers, servers, VoIP phones, guest Wi-Fi, printers, cameras, and IoT devices.
The key point is that separation alone is not enough. Real segmentation also defines the rules between those segments. Your accounting PCs may need access to an ERP server but not to security cameras. Guest devices may need internet access but nothing internal. Printers might need to receive jobs from employee PCs but should not be able to initiate traffic to domain controllers.
That is where many small businesses get it wrong. They create a guest SSID and assume the job is done. In reality, good segmentation is less about naming networks and more about controlling traffic between them.
How to segment office network without overcomplicating it
The cleanest approach is to start with a simple trust model. Ask which devices are most sensitive, which are least trusted, and which traffic is actually required for work. Once you answer that, the technical design becomes much easier.
A typical small or midsize office can start with five practical segments. One for employee workstations, one for servers and core infrastructure, one for voice devices, one for printers and shared peripherals, and one for guests or unmanaged devices. If the office relies heavily on cameras, smart TVs, badge readers, or building controls, those usually deserve their own segment too.
VLANs are the most common way to create those segments on a business network. A managed switch can assign ports to different VLANs, and a business-grade access point can map multiple SSIDs to separate VLANs for wireless users. From there, a router or firewall handles traffic between VLANs and applies access rules.
For a smaller office, this can stay fairly lean. You do not need enterprise-level complexity to get real value. But you do need gear that supports managed switching, VLAN tagging, and firewall policies. Consumer networking hardware often falls short here, especially when you need clear inter-VLAN controls.
Start with assets, not hardware
Before buying anything or changing switch settings, inventory what is already on the network. That means endpoints, servers, printers, wireless devices, phones, cameras, cloud-managed appliances, and anything installed by a vendor years ago that nobody documented properly.
This step matters because segmentation designed from assumptions usually breaks something. Maybe a copier needs to scan to a file server. Maybe door access controllers rely on a cloud service plus a local management workstation. Maybe your phone system still uses a desktop app that talks to a PBX on a strange port. If you skip discovery, those dependencies turn into support tickets later.
A simple asset list with device type, owner, IP information, and communication needs is enough to begin. You are not trying to build a perfect CMDB. You are trying to understand what belongs together and what absolutely should not.
Build segments around risk and function
There are two common ways to segment an office: by business role or by device category. Most organizations end up using a mix of both.
By role works well when departments handle very different data. Finance, HR, engineering, and general office users may each have distinct access needs. By device category works well for security and operations. Servers, workstations, printers, cameras, and guest devices all behave differently and carry different risk.
For many SMBs, device-based segmentation is the best first move because it is easier to enforce and troubleshoot. A camera VLAN is easy to understand. A printer VLAN is easy to lock down. Guest Wi-Fi isolation is straightforward. Department-based segmentation can come later if compliance, data sensitivity, or internal risk justifies it.
The trade-off is policy sprawl. The more segments you create, the more rules you have to maintain. Too few segments leaves the network exposed. Too many creates administrative drag. If your team is small, start with the biggest risk boundaries first and expand only when there is a clear reason.
Use the firewall as the traffic cop
This is the part that turns segmentation from a layout into a security control. Once VLANs exist, the firewall should decide what crosses between them. The default mindset should be deny by default, then allow only what is necessary.
For example, employee PCs may need DNS, DHCP, internet access, authentication services, and access to specific application servers. Guest devices should get internet only. Printers may need inbound access from user subnets but little or no outbound access beyond updates or management. Cameras often need access to an NVR, not to user laptops.
A lot depends on the firewall itself. Some entry-level firewalls can route VLANs but make policy management painful. Others offer layer 7 controls, identity awareness, logging, and easier rule organization. If you are redesigning an office network, this is one place where saving money can cost you time later.
Logging matters too. If you block traffic between segments, you need enough visibility to know whether you stopped a threat or broke a legitimate workflow.
Wired and wireless should follow the same logic
Many offices get the wired network mostly right, then let Wi-Fi become a free-for-all. That defeats the point. If staff devices on Ethernet are in one policy zone but staff laptops on Wi-Fi land somewhere else, your design is inconsistent from the start.
Your wireless setup should mirror the same segmentation strategy. Staff SSIDs should map to the employee VLAN, guest SSIDs should map to an isolated guest VLAN, and IoT or facilities devices should use their own wireless segment when possible. Better still, use WPA3-Enterprise or at least strong WPA2/WPA3 business authentication for staff access instead of a shared password that never changes.
If you support bring-your-own-device access, do not let personal phones ride on the same network as managed corporate laptops unless you have mobile device controls that justify it.
Test dependencies before you lock it down
Segmentation projects often fail in the last 10 percent. The VLANs are created, the policies look sensible, then suddenly phones cannot register, scans fail, or a line-of-business app stops working.
That is normal. Office networks are full of hidden dependencies, especially in environments that grew over time. The fix is not to abandon segmentation. The fix is staged testing.
Roll out one segment at a time. Move low-risk devices first. Validate DHCP, DNS, internet access, application reachability, printing, file shares, voice traffic, and remote management. Watch logs. Then tighten rules. If you start permissive and reduce access methodically, you are less likely to cause a major disruption than if you go straight to a highly restrictive model without testing.
This is also where documenting rules pays off. Every allow rule should have a reason. If nobody can explain why a camera network needs access to a workstation subnet, that rule probably should not exist.
Common mistakes that weaken segmentation
The biggest mistake is routing everything everywhere because users complained once. That turns segmented VLANs back into a flat network with extra steps.
Another common issue is mixing critical infrastructure with commodity devices. Domain controllers, backup appliances, hypervisors, and management interfaces should not sit next to printers and conference room hardware. Management access deserves tighter controls than general production traffic.
There is also the false sense of security problem. VLANs are useful, but they are not magic. If inter-VLAN traffic is wide open, the network is still effectively flat. Likewise, segmentation does not replace endpoint security, patching, MFA, backups, or proper monitoring. It reduces blast radius. It does not eliminate risk.
Finally, avoid designing around your current floor plan instead of business need. Just because devices are in the same room does not mean they belong on the same segment.
When microsegmentation makes sense
For most offices, traditional VLAN-based segmentation is enough. But if you manage sensitive workloads, hybrid infrastructure, or stricter compliance requirements, microsegmentation can be worth considering.
That usually means applying policy closer to the workload or host level rather than relying only on network boundaries. It gives you more granular control, especially in virtualized or cloud-connected environments. The downside is complexity. It demands stronger visibility, better policy discipline, and more mature operations. If your team is still working through unmanaged switches and ad hoc Wi-Fi, this is probably not the first step.
A smarter path is to get the office core right first, then add finer-grained controls where they solve a specific risk.
What a good result looks like
A well-segmented office network feels boring in the best possible way. Guests get online without seeing anything internal. Printers work, but they do not have broad access. Cameras stay in their lane. Staff can reach the systems they need, and malware on one endpoint has fewer paths to spread.
That is the outcome to aim for – not maximum complexity, but clear boundaries that match how your business actually works. If you are planning changes, start with the biggest trust gaps, document what talks to what, and let the firewall enforce the rules. A smaller, smarter network beats a bigger flat one every time.